
Sophos Firewall (BYOL) Provisioning Workflow on MTN Cloud
Overview
This guide covers the automated deployment of a Sophos Firewall instance on the MTN Cloud Platform using the Bring Your Own Licence (BYOL) model. Sophos Firewall provides comprehensive network security, including next-generation firewall (NGFW), intrusion prevention, web filtering and advanced threat protection capabilities.
Why it matters:
- Comprehensive Network Security: Protects your cloud infrastructure with next-generation firewall capabilities, including application control, intrusion prevention and web filtering.
- Advanced Threat Protection: Detects and blocks sophisticated threats, including ransomware, malware and zero-day attacks using advanced threat intelligence.
- Centralised Management: Manage multiple firewalls from a single console using Sophos Central, simplifying administration and policy management.
- Flexible Licensing: The BYOL model allows you to leverage your existing Sophos licences, providing cost flexibility and integration with your existing Sophos infrastructure.
- VPN Connectivity: Provides robust VPN capabilities for secure remote access and site-to-site connectivity, enabling secure hybrid cloud deployments.
- Traffic Visibility: Gain deep visibility into network traffic, application usage and user activity with comprehensive logging and reporting.
Prerequisites
Before you begin, ensure you have:
- An active MTN Cloud Console login with appropriate permissions to view Provisioning and Infrastructure tabs.
- A Resource Pool (Project) already created.
- A Network already created.
- A Router already created with the network attached.
- A pre-configured Security Group to manage inbound/outbound traffic.
- A valid licence key or a free-trial licence for initial activation.
- A planned deployment strategy, including:
- Resource specifications (CPU, RAM, storage).
- LAN and WAN network assignments.
- IP addressing requirements.
- Required inter-communication and associated Security Group rules.
- Whether a floating IP is needed.
Tip: If you do not see your networks or Security Groups during provisioning, refresh the portal or contact support.
Important Note: The order in which you add networks during provisioning matters. Sophos takes the first network as the LAN (protected) side and the second as the WAN (outside) side. Always add the LAN network first.
Minimum System Requirements
Select a Plan and Volume that meet or exceed these figures. The recommended MTN catalog plan is shown for convenience.
- vCPU: 2 vCPU (minimum).
- Memory (RAM): 4 GB (minimum, 8+ GB recommended).
- Disk Storage: 40 GB dedicated disk (minimum).
- MTN Catalog Plan: G2S4 (2 vCPU / 4 GB).
- Interfaces: 2 interface minimum (LAN and WAN).
Important Note: The disk size you choose is only the firewall’s main disk. A second 80 GB disk (used by the firewall to store logs and reports) is added for you automatically, so the total is the storage you select plus 80 GB.
Phase 1 – Create Linux/Windows User
Purpose: Configure user credentials that will be used to access the Sophos instance via the console.
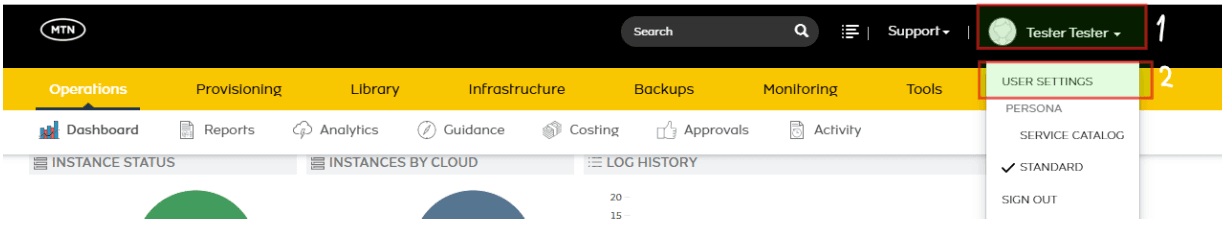
Navigate to User Settings
Navigate to User Settings by clicking the dropdown beside your name at the top right corner of the screen.
Configure User Credentials
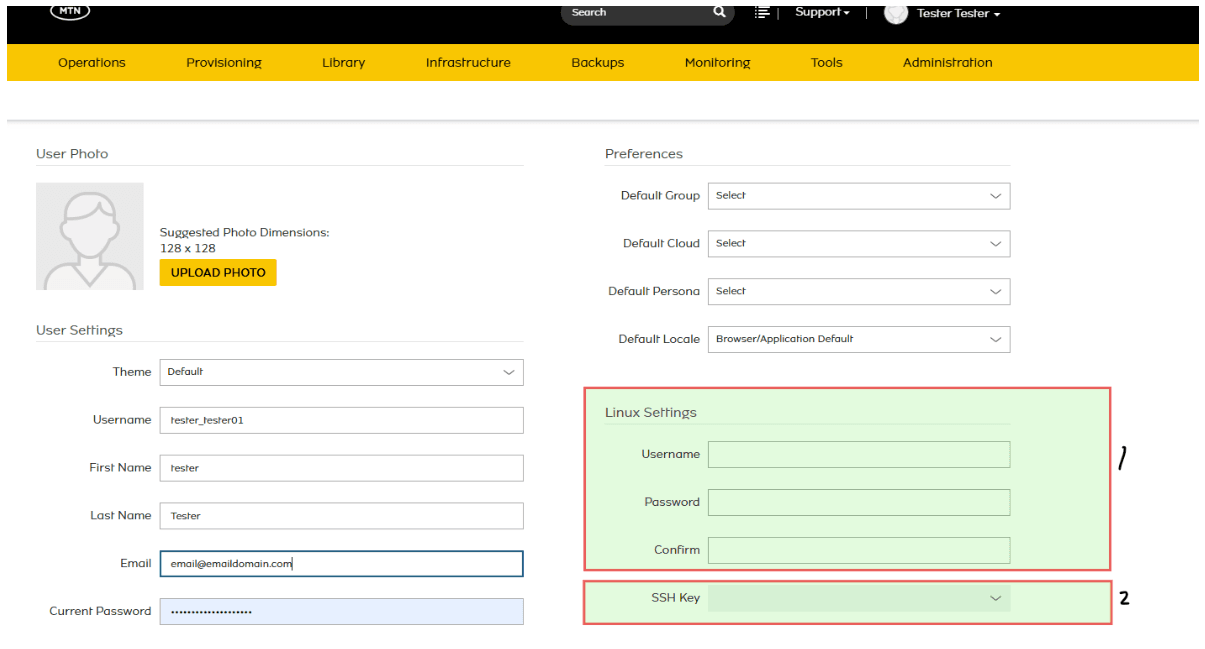
Locate the Linux Settings section and assign the following:
- Username: Enter a username for Linux access.
- Password: Enter a strong password.
- Confirm Password: Re-enter the password to confirm.
- SSH Key: Optionally, select an existing SSH key pair if you have one configured.
Repeat the same process for your Windows Settings if required. Once all details are entered, scroll to the bottom of the page and click Save.
Phase 2 – Define Security Groups
Purpose: Control network access to (ingress) and from (egress) your Sophos instance.
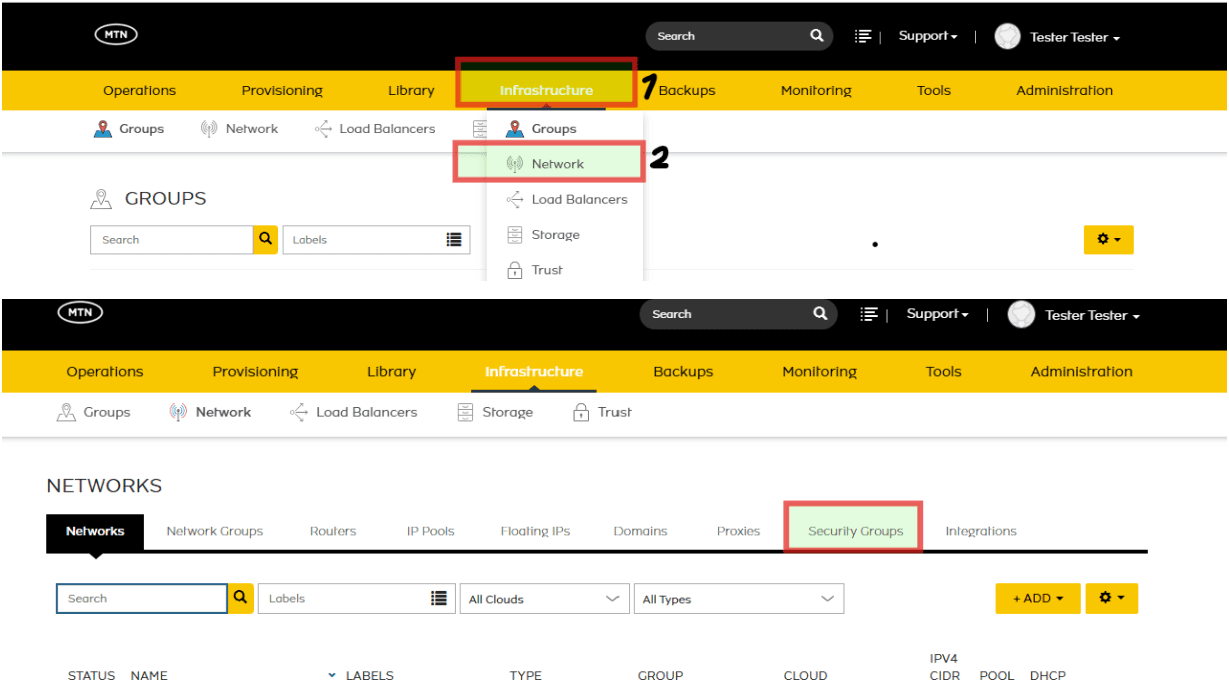
Navigate to Security Groups
Navigate to Infrastructure > Network > Security Groups.
Create Security Group
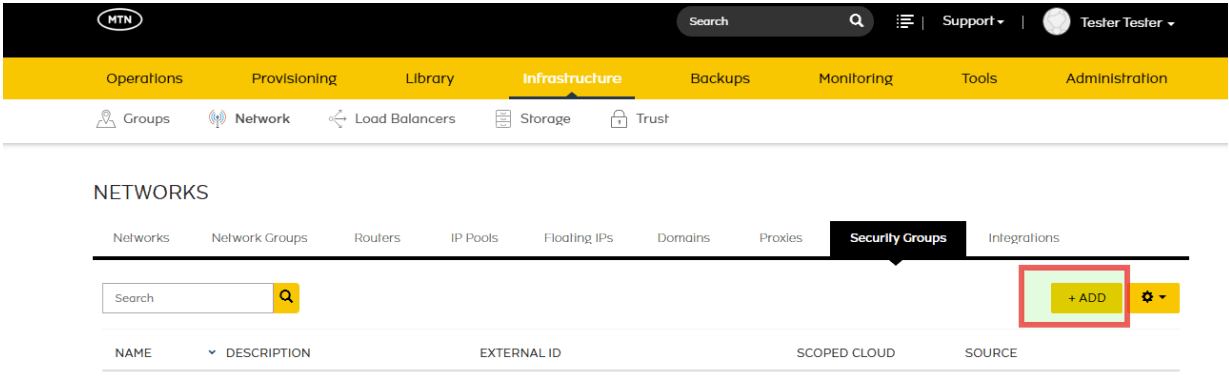
Click + Add and assign the following details:
- Name: Enter a descriptive name for your Security Group.
- Description: Provide a brief description of the group’s purpose.
- Scoped Cloud: Select the appropriate cloud (e.g. MTNNG_CLOUD_AZ_1).
Configure Security Group Rules
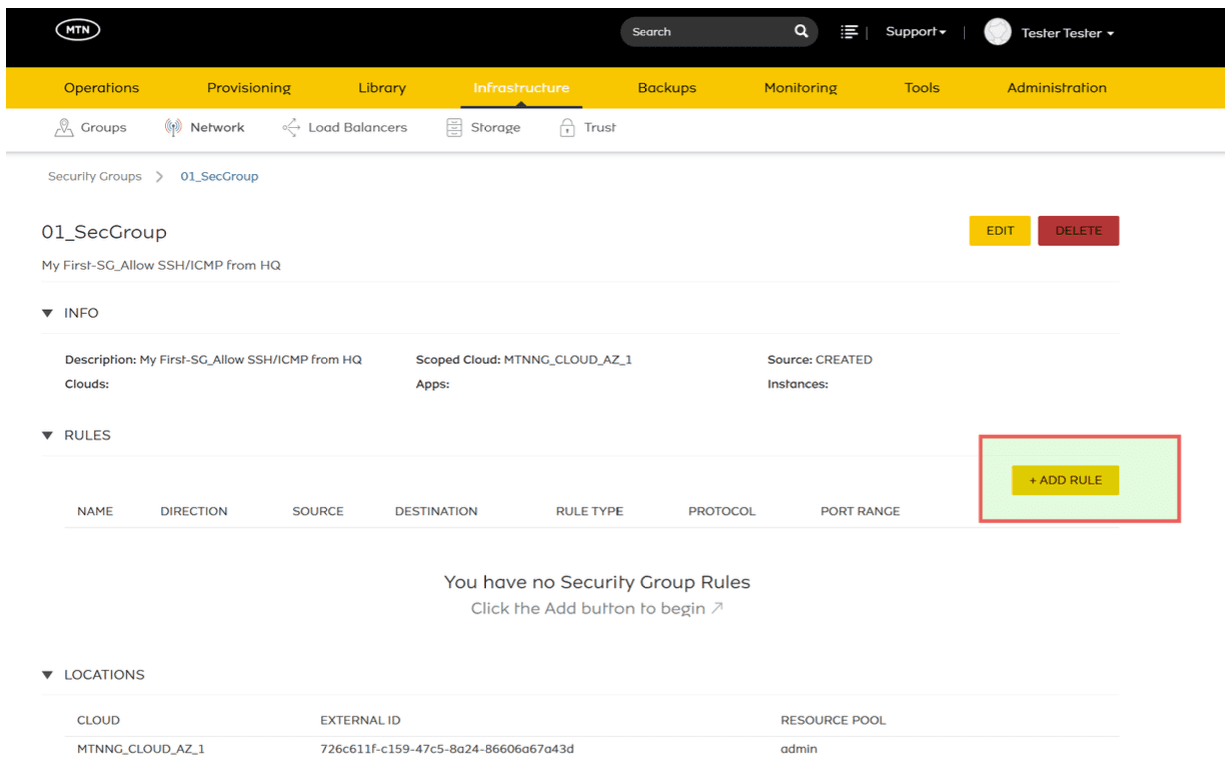
- Click on the newly created Security Group.
- Navigate to the Rules tab.
- Click + Add Rules and assign the following:
- Name: Enter a descriptive rule name.
- Direction: Ingress (inbound) or Egress (outbound).
- Rule Type: Select Custom Rule.
- Protocol: Choose TCP, UDP or ICMP.
- Port Range: Specify the port range (e.g. 22 for SSH, 443 for HTTPS).
- Source Type: Define the source (e.g. Network, IP or Security Group).
- Source: Enter the source IP or CIDR range.
- Destination Type: Define the destination.
- Destination Port Range: Specify the destination port range.
- Scroll down and click Save Changes.
- Navigate to the Location tab, click + Add Location and select the cloud where the workload will be provisioned.
- Click Save Changes.
Use Case – Restricting Access to Only My Laptop
Scenario: You want only your laptop (with public IP 200.200.113.15) to be able to access your Sophos instance. All other devices should be blocked.
Create the Laptop-Access-Only Security Group
- Navigate to Infrastructure > Network > Security Groups.
- Click + Add and assign:
- Name: Laptop-Access-Only
- Description: Allow secure remote access only from my laptop
- Scoped Cloud: Select the specific Availability Zone (e.g. MTNNG_CLOUD_AZ_1).
- Select the Laptop-Access-Only group.
- Go to the Rules tab and add the rules described below.
Add the Laptop Access Rules
Each rule uses Direction: Ingress, Rule Type: Custom Rule, Source Type: Network, Source: 200.200.113.15/32 and Destination Type: Instance.
- Allow-SSH-From-Laptop: Protocol TCP, Port Range 22, Destination Port Range 22.
- Allow-GUI-From-Laptop: Protocol TCP, Port Range 443, Destination Port Range 443.
- Allow-SNMP-From-Laptop: Protocol UDP, Port Range 161, Destination Port Range 161.
- Allow-ICMP-From-Laptop: Protocol ICMP.
- Allow-WebAdmin-From-Laptop: Protocol TCP, Port Range 4444, Destination Port Range 4444.
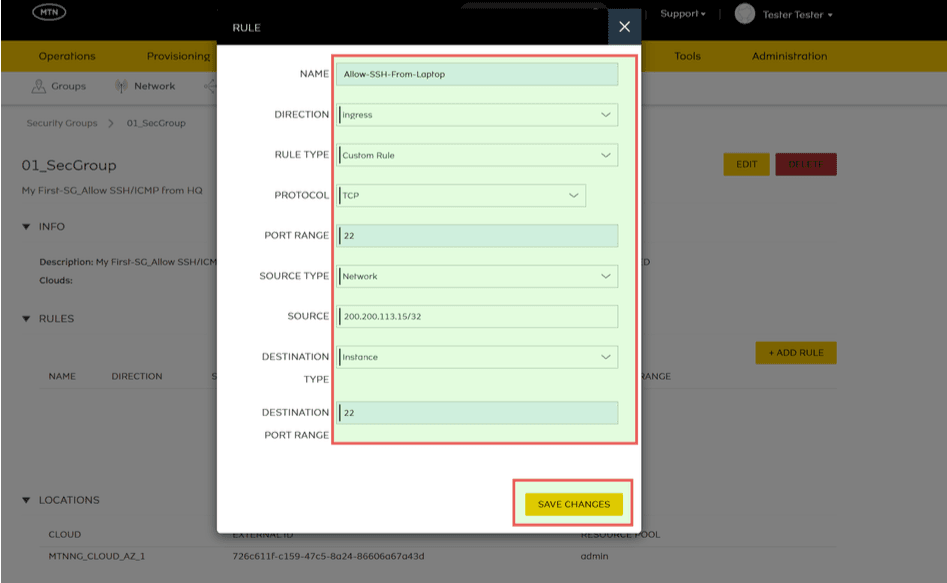
Click Save Changes, then attach the Laptop-Access-Only group to your Sophos instance in addition to the default Security Group.
Result: Only your laptop can successfully access the Sophos instance on the open ports. All other attempts are denied.
Phase 3 – Provision the Sophos Instance (BYOL)
Purpose: Deploy a Sophos Firewall instance with your configured Security Groups and network settings.
Navigate to Catalog
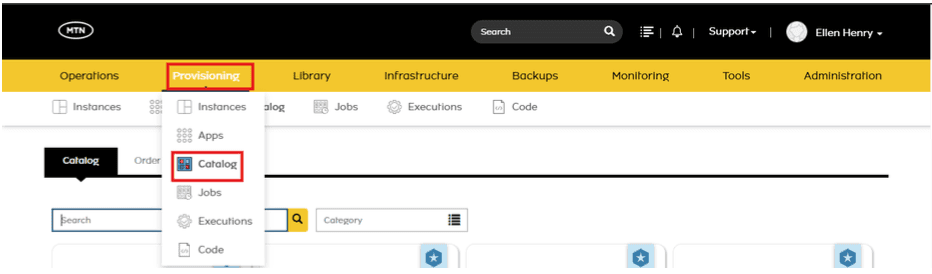
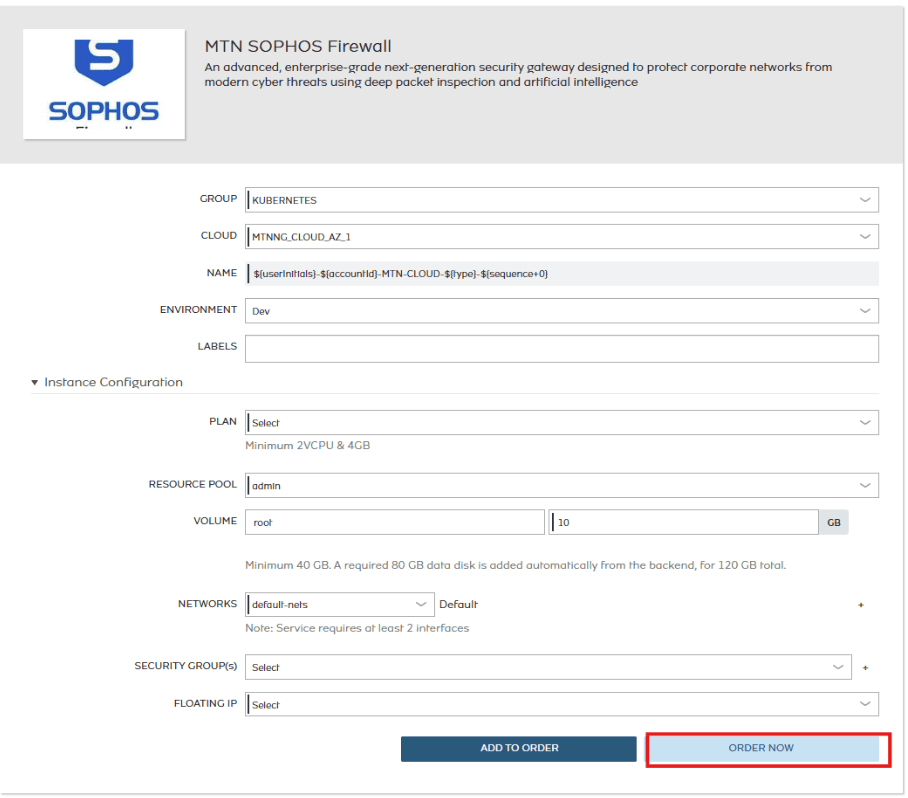
- Navigate to Provisioning > Catalog.
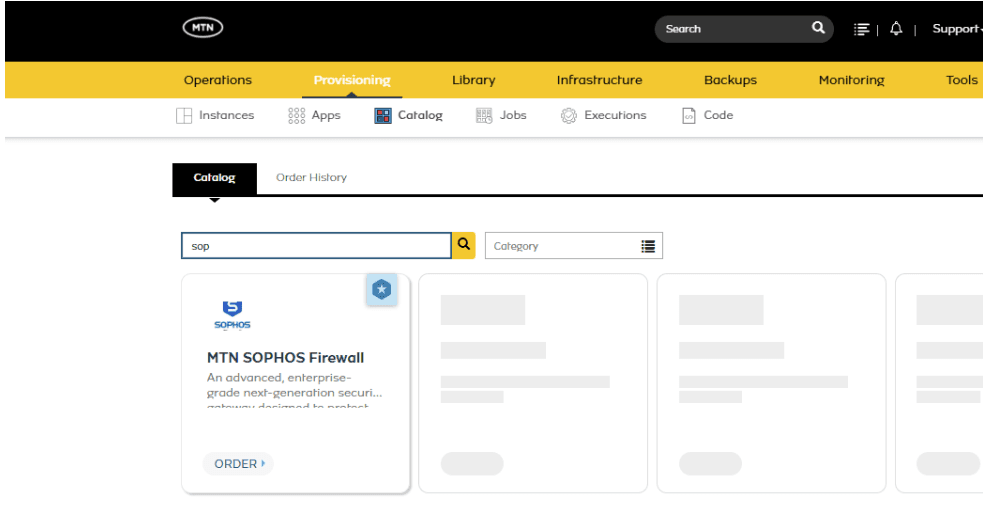
- Search for and click MTN Sophos Firewall (BYOL).
- Click Order to begin provisioning.
Configure Deployment
Fill in the following details in the order form.
General Configuration:
- Group & Cloud: Select your assigned group and cloud (e.g. MTNNG_CLOUD_AZ_1).
- Name: Provide a unique name for your Sophos instance.
- Environment: Select the appropriate environment (e.g. Development, Staging, Production).
- Labels: Optionally, add labels for organisational purposes.
Instance Configuration:
- Resource Pool: Choose the appropriate Resource Pool (Project).
- Plan: Select a plan that meets the minimum requirements (minimum 2 vCPU and 4 GB RAM). Recommended: G2S4 (2 vCPU / 4 GB) or larger.
- Volume: Select the required volume capacity (main disk). Minimum 40 GB. A second 80 GB disk is added automatically for logs and reports.
- Networks: Add your networks. Add your LAN network first, then your WAN network second.
- Floating IP: Assign a floating IP if required (on the WAN network for external access).
- Security Groups: Select both the Default Security Group and the custom Security Group created earlier.
Click Order Now to initiate the deployment. MTN Cloud will provision and display the instance status once deployment is complete.
Initial Network Configuration
Important: Every new Sophos Firewall starts with the same factory address, 172.16.16.16. Change it to an address that belongs to your LAN network; otherwise, your computers and the firewall will not be able to find each other.
Set the Firewall’s LAN Address
- Open your firewall instance in the console.
- Click the Network tab and note the IP address shown for the first interface (eth0). You will type this exact address in the steps below.
- Open the Console tab of your firewall.
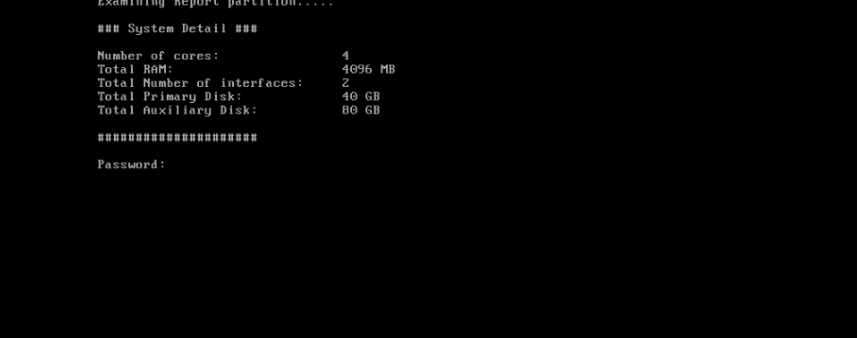
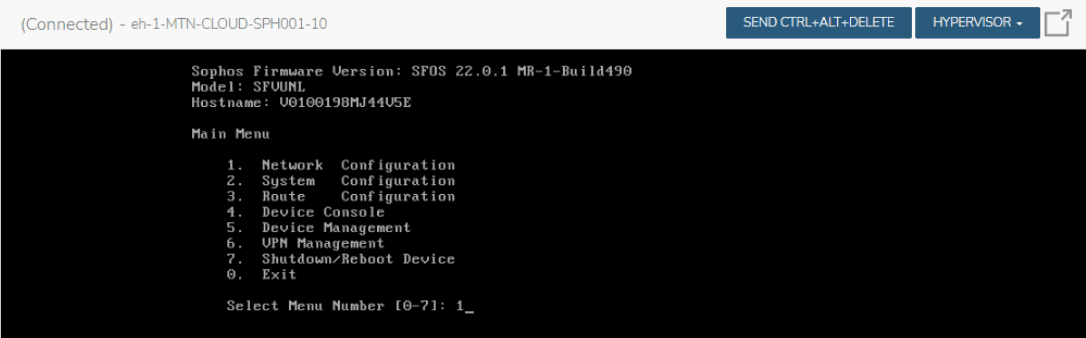
- At the Password: prompt, type the default password and press Enter. You will see a numbered menu.
- Type 1 and press Enter – this opens Network Configuration.
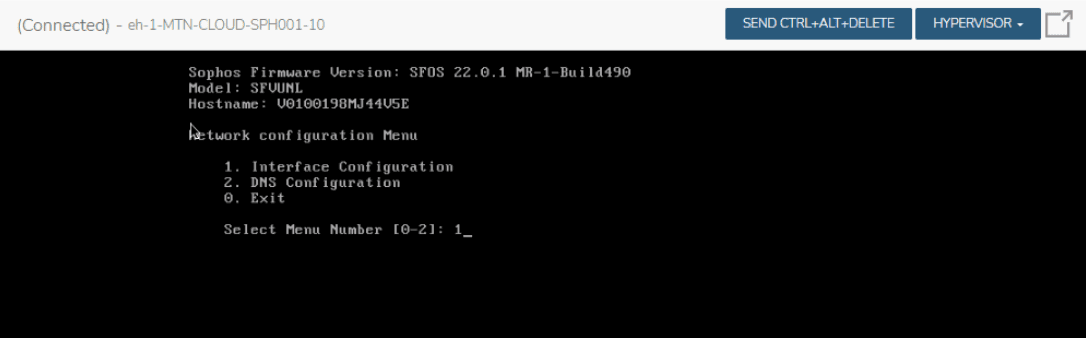
- Type 1 again and press Enter – this opens Interface Configuration.
- Press Enter at both Port A & B prompts.
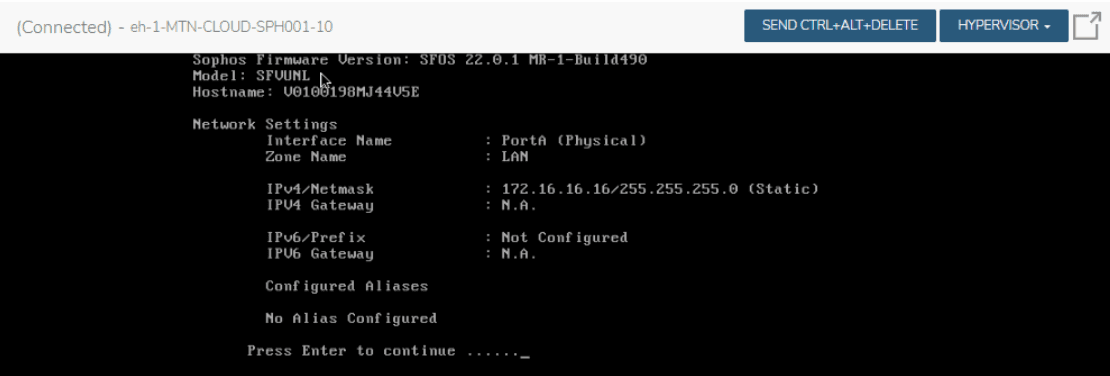
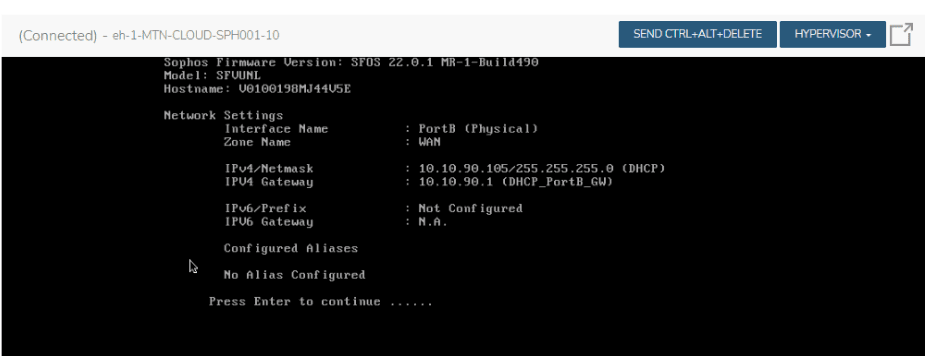
- It asks Set IPv4 Address (y/n). Type y and press Enter.
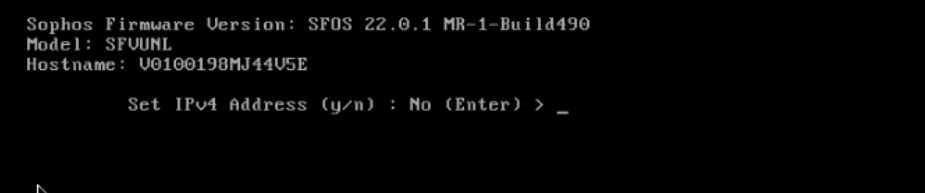
- Type the LAN address you noted earlier (for example 192.168.141.67) and press Enter.
- Type the network mask when asked – usually 255.255.255.0 – press Enter.
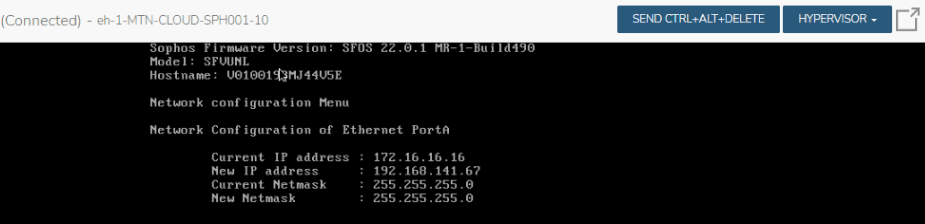
- It asks Set IPv6 Address (y/n). Unless you specifically use IPv6, just press Enter to accept No.
- Type 0 and press Enter to step back out of the menus. The firewall applies the new address.
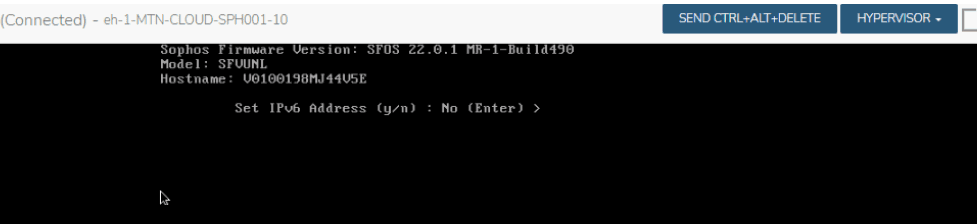
Note: The firewall only accepts management connections from a computer on the same LAN network as itself. By default, you cannot reach it directly from the public internet. To access it, use a computer on the same LAN network as the firewall, or a secure management connection into your MTN Cloud environment (e.g. management bastion or VPN).
Access the Sophos Firewall Management GUI
- From a computer on the same LAN, open a web browser and go to https://<your-firewall-LAN-address>:4444 (for example https://192.168.141.67:4444).
- Your browser will show a security warning (this is normal for a new firewall). Click Advanced.
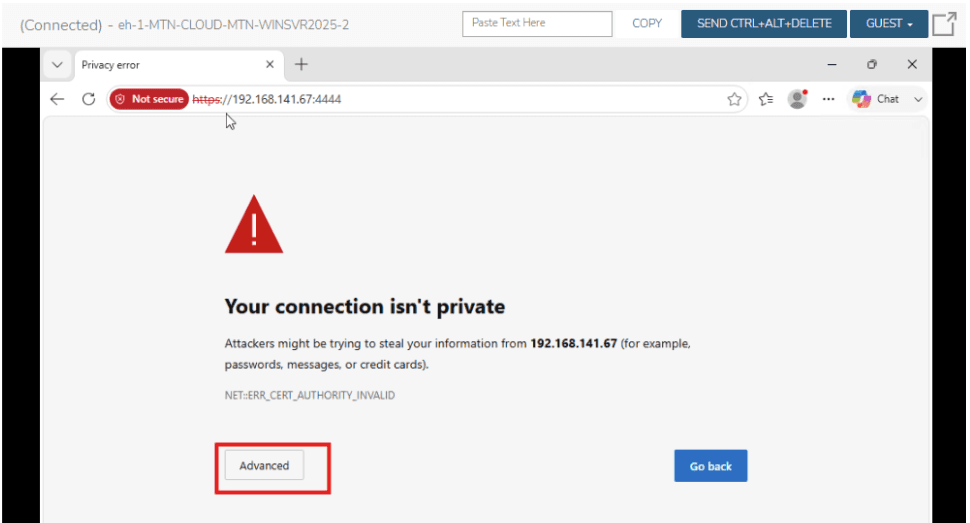
- Click Continue / Proceed to the address.
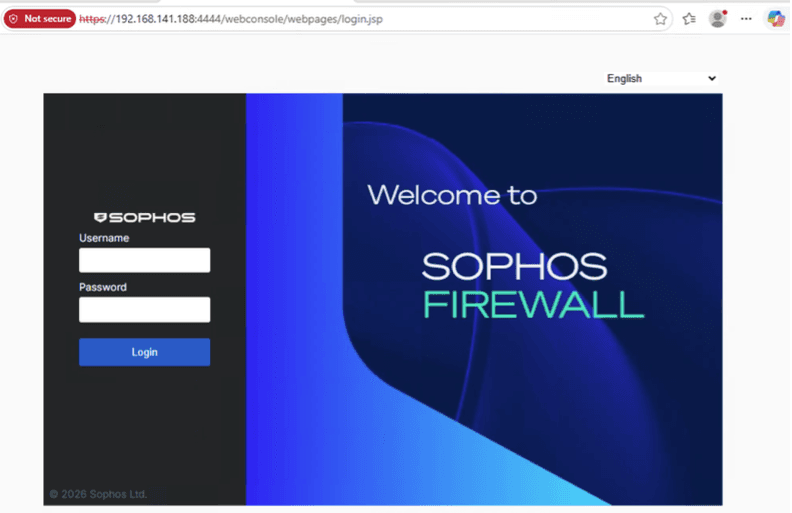
Default Credentials:
Username: admin
Password: Passw0rd@123
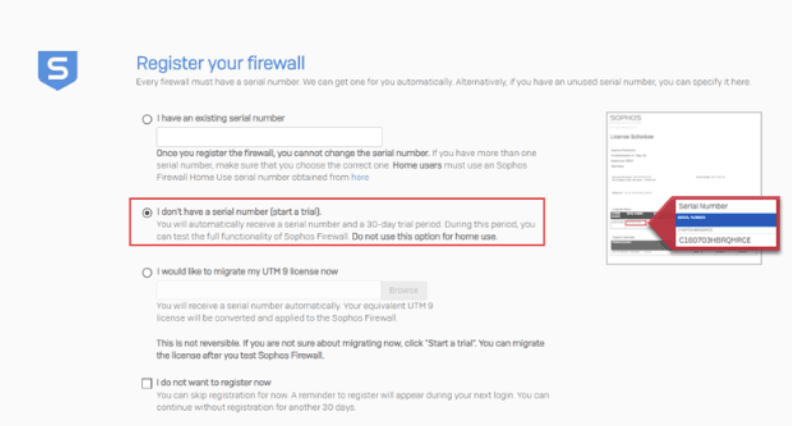
Important: It is highly recommended to change the default password immediately upon first login and store the new credentials securely. After logging in, register your licence or log in to an existing account.
Important Tips and Notes
- Network Order: The order in which you add networks during provisioning matters. Sophos takes the first network as the LAN (protected) side and the second as the WAN (outside) side. Always add the LAN network first.
- License Activation: This is a Bring Your Own Licence (BYOL) instance. On first login, you will be prompted to register a licence. You can choose “I do not want to register now” to continue – you have up to 30 days to register later.
- Change Default Password: Change the default password immediately after your first login and store the new password securely.
- Additional Disk: The disk size you choose is only the firewall’s main disk. A second 80 GB disk (used by the firewall to store logs and reports) is added for you automatically, so the total is the storage you select plus 80 GB.
- Management Access: For security, the firewall only accepts management connections from a computer on the same LAN network as itself. Use a management bastion or VPN if you need to access it remotely.
- Naming Conventions: Use consistent names for keys, networks and instances to simplify management.
- Documentation: Keep a record of IP addresses, credentials and assigned resources for future reference.
- Security Groups: Regularly review and update rules to follow the principle of least privilege.
- Reusability: You may reuse Security Groups and username/password configurations for subsequent Sophos deployments based on your security considerations.
- Troubleshooting: If something does not appear or connect as expected, refresh the portal first, then contact MTN Cloud Support.