
Site-to-Site IPsec VPN Configuration Guide on MTN Cloud
IPsec Tunnel Between Two Cloud Tenants. Service Name: MTN Cloud VPN — Service Category: Security / VPN.
Important
The configuration must be completed on BOTH tenants. Where configuration values differ between Tenant A and Tenant B, the respective values are shown. Replace the example IP addresses with the addresses used in your deployment.
Overview
A site-to-site IPsec VPN establishes an encrypted network tunnel between two MTN Cloud tenants, allowing private networks in each tenant to communicate securely. This configuration uses an MTN Cloud VPN instance in each tenant to route traffic between the two LAN environments.
Why it matters
- Enables secure communication between private networks across separate cloud tenants.
- Keeps Linux VM instances on private LAN networks without exposing them directly to the public internet.
- Uses IPsec encryption to protect traffic between the two tenant environments.
- Provides centralized routing and firewall control through the MTN Cloud VPN instances.
Prerequisites
Before beginning the configuration, ensure that:
- Access is available to both MTN Cloud tenants involved in the VPN connection.
- The required tenant group and cloud networking permissions are available.
- A public/WAN network and private/LAN network can be created in each tenant.
- A router with an associated floating IP is available for the WAN network.
- Private CIDR ranges have been selected for both tenants and do not overlap.
- An MTN Cloud VPN instance and Linux VM can be provisioned in each tenant.
- A security group is already defined for the deployment. For guidance on creating one, reference the security group creation documentation.
- The floating IP addresses and private LAN IP addresses for both MTN Cloud VPN instances can be identified during deployment.
Tip
If required networking or VPN features are not visible in the portal, refresh the portal and verify that the correct tenant and permissions are being used. Contact support if the required features remain unavailable.
Important Note
The security group must allow the VPN traffic required by the deployment. The source specifies TCP ports 22 and 443, ICMP, and UDP ports 500, 4500, and 1194. UDP ports 500 and 4500 are required for IPsec/IKE traffic, while UDP 1194 is included in the source security-group configuration.
Create the WAN Network
Navigation: Infrastructure → Networks → Create Network
Create the public-facing network that will provide connectivity to the MTN Cloud VPN instance. Configure the following:
- Set Group to your tenant group.
- Enter a descriptive Name.
- Set a CIDR appropriate for the public subnet.
- Attach a Gateway.
- Attach the network to a Router that has a floating IP associated with it.
- Ensure DHCP Server is checked.
- Click Save.
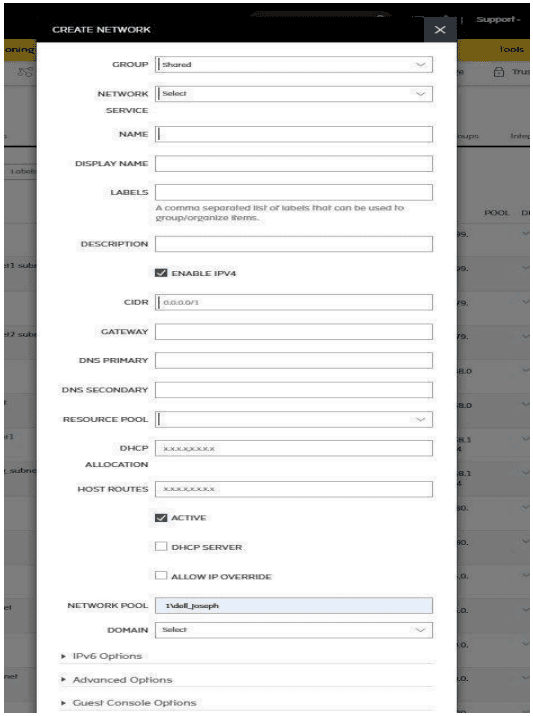
Figure 1 — Create Network form showing the fields used to configure the public WAN network
Create the LAN Network
Navigation: Infrastructure → Networks → Create Network
Create the private network that will connect the MTN Cloud VPN instance to the Linux VM. Configure the following:
- Set Group to your tenant group.
- Enter a descriptive Name.
- Set CIDR to the chosen private range (Example for Tenant A: 10.10.40.0/24; Example for Tenant B: 192.168.19.0/24).
- Input the Gateway.
- Check DHCP Server and Override IP so that IPs can be statically assigned.
- Click Save.
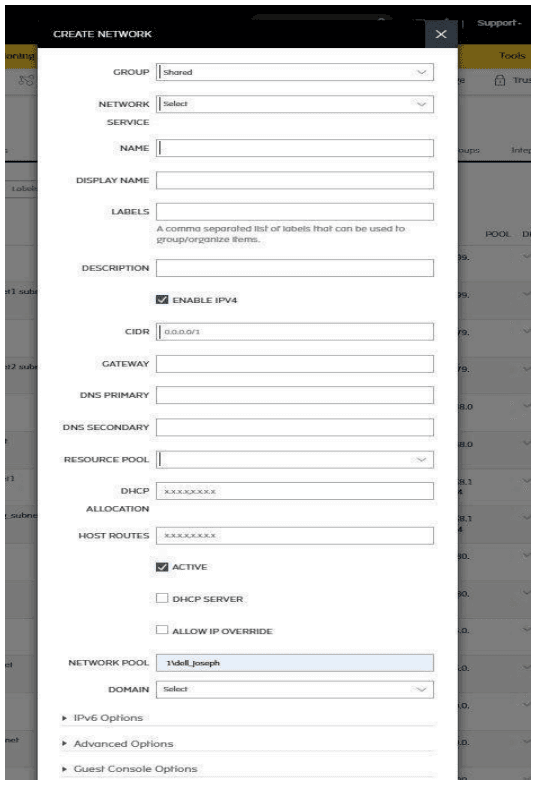
Figure 2 — Create Network form showing the fields used to configure the private LAN network
Attach the WAN Network to a Router
Navigation: Infrastructure → Network Routers → Add Network Router
Ensure that the WAN network is connected to a router that routes to the public floating IP. Select the appropriate external network from the cloud provider’s public network pool.
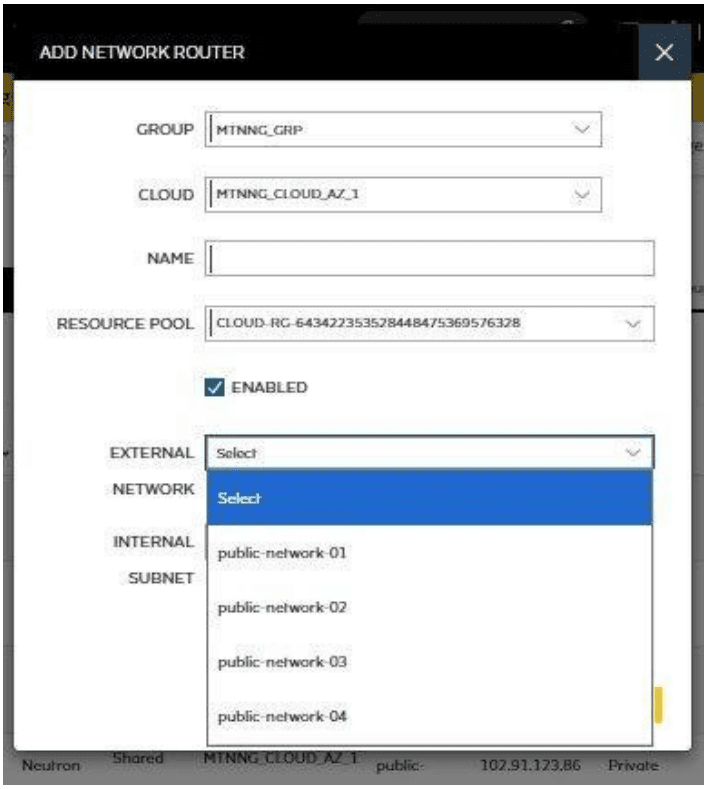
Figure 3 — Network router configuration showing the WAN network connected to the external public network
Deploy the MTN Cloud VPN and Linux Instances
Navigation: Provisioning → Catalog → MTN VPN Services (MTN Cloud VPN)
Deploy the MTN Cloud VPN Instance
When provisioning the MTN Cloud VPN instance, attach both networks created in the previous sections. The order is important: the WAN network must be configured as the primary eth0 interface. Configure the interfaces as follows:
| Interface | Network | Configuration |
|---|---|---|
| Primary (eth0 / WAN) | Public network | Select the public network attached to the router |
| Secondary (eth1 / LAN) | Private LAN network | Select the private LAN network with no router |
Also:
- Attach the security group defined for the deployment.
- Note the private IP assigned to eth1 by the cloud platform. This IP will be required when configuring the LAN interface.
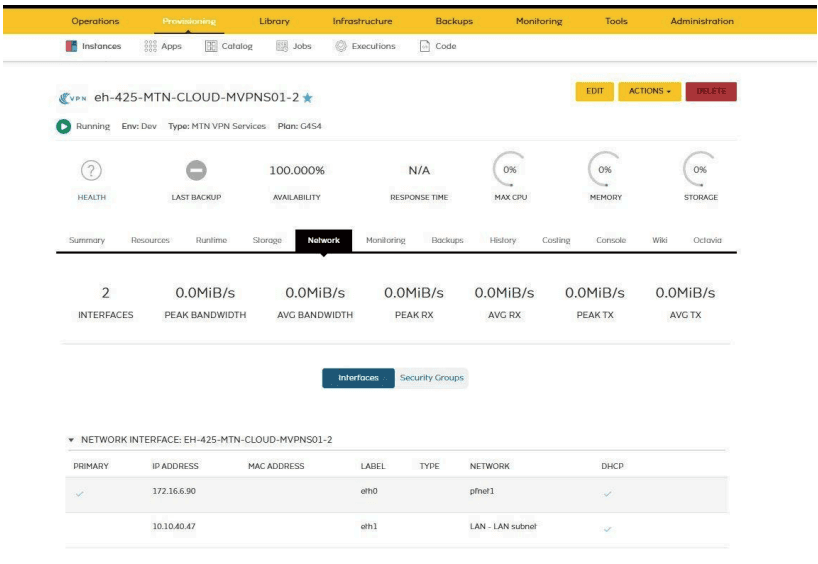
Figure 4 — MTN Cloud VPN instance Network tab showing the WAN interface with a public IP and the LAN interface with a private IP
Deploy the Linux VM
Deploy the Linux test VM using only the private LAN network. Do not attach a floating IP to the VM; external and cross-tenant traffic must route through MTN Cloud VPN. Configure the VM as follows:
- Attach only the private LAN network as eth0.
- Attach the same security group used for the MTN Cloud VPN instance.
- Note the private IP assigned to the VM by the cloud platform.
Warning
Do NOT attach the public WAN network to the Linux VMs. All internet and cross-tenant traffic must route through the MTN Cloud VPN firewall.
Configure the MTN Cloud VPN LAN Interface
Navigation: MTN Cloud VPN GUI → Interfaces → LAN (vtnet1)
- Access the MTN Cloud VPN GUI through the floating IP assigned to the WAN interface. The source specifies the default credentials as admin / cloud.
- Configure the LAN interface using the static IP assigned to eth1 during deployment.
Set the LAN Interface IP
Navigation: Interfaces → LAN. Configure the following:
| Field | Value |
|---|---|
| IPv4 Configuration Type | Static IPv4 |
| IPv4 Address | IP assigned to eth1 during deployment |
| IPv4 Upstream Gateway | None |
Important Note
The IPv4 Upstream Gateway for the LAN interface must remain set to None.
Configure IPsec Phase 1
Navigation: MTN Cloud VPN GUI → VPN → IPsec → Tunnels → Add P1
Phase 1 establishes the IKE (Internet Key Exchange) session between the two MTN Cloud VPN instances. The Phase 1 settings must match on both tenants, except that the identifiers and remote gateway IP addresses are swapped between Tenant A and Tenant B.
Phase 1 Settings
Select Add P1 on the Tunnels tab and configure:
| Field | Value |
|---|---|
| Key Exchange Version | IKEv2 |
| Internet Protocol | IPv4 |
| Interface | WAN |
| Remote Gateway | Floating IP of the remote MTN Cloud VPN |
| Description | Tenant-Tenant or another descriptive name |
| Authentication Method | Mutual PSK |
| My Identifier | IP Address — enter your floating IP |
| Peer Identifier | IP Address — enter the remote floating IP |
| Pre-Shared Key | Strong random key, identical on both tenants |
| Encryption Algorithm | AES 128 bits |
| Hash Algorithm | SHA256 |
| DH Group | 14 (2048 bit) |
| Lifetime | 28800 seconds (8 hours) |
| NAT Traversal | Auto |
| Dead Peer Detection | Enabled; Delay: 10, Max Failures: 5 |
Important Note
The Pre-Shared Key must be identical character-for-character on both MTN Cloud VPN instances. The source recommends generating a strong random key of at least 32 characters and copying it carefully to both tenants.
Configure IPsec Phase 2
Navigation: MTN Cloud VPN GUI → VPN → IPsec → Tunnels → Show Phase 2 Entries → Add P2
Phase 2 defines the encrypted data channel, including the subnets permitted to communicate through the tunnel and the encryption used to protect the traffic. The local and remote network values must use subnet base addresses, not individual host addresses.
Phase 2 Settings
| Field | Tenant A | Tenant B |
|---|---|---|
| Mode | Tunnel IPv4 | Tunnel IPv4 |
| Local Network Type | Network | Network |
| Local Network Address | 10.10.40.0/24 | 192.168.19.0/24 |
| NAT/BINAT Translation | None | None |
| Remote Network Type | Network | Network |
| Remote Network Address | 192.168.19.0/24 | 10.10.40.0/24 |
| Protocol | ESP | ESP |
| Encryption Algorithms | AES 128-bit + AES128-GCM 128-bit | AES 128-bit + AES128-GCM 128-bit |
| Hash Algorithms | SHA256 | SHA256 |
| PFS Key Group | 14 (2048 bit) | 14 (2048 bit) |
| Lifetime | 3600 seconds (1 hour) | 3600 seconds (1 hour) |
After saving both Phase 1 and Phase 2, click Apply Changes. Navigate to Status → IPsec and click Connect to initiate the tunnel. Both Phase 1 and Phase 2 should show as Established.
Critical
The Local Network and Remote Network addresses must be the subnet base addresses with the correct prefix length. For example, use 10.10.40.0/24, not a host address such as 10.10.40.47/32. Using a host IP can cause Phase 2 to fail or result in a traffic-selector mismatch.
Configure Firewall Rules
WAN Firewall Rules
Navigation: MTN Cloud VPN GUI → Firewall → Rules → WAN
Add the required WAN firewall rule to permit IPsec encrypted traffic to reach the MTN Cloud VPN instance from the internet.
| Protocol | Destination Port | Description |
|---|---|---|
| IPv4 ESP | Any | Allow ESP encrypted packets |
IPsec Firewall Rules
Navigation: MTN Cloud VPN GUI → Firewall → Rules → IPsec
Add two rules to permit bidirectional traffic between the two tenant subnets.
| Action | Protocol | Source | Destination | Description |
|---|---|---|---|---|
| Pass | IPv4 Any | 10.10.40.0/24 | 192.168.19.0/24 | Allow Tenant A to Tenant B |
| Pass | IPv4 Any | 192.168.19.0/24 | 10.10.40.0/24 | Allow Tenant B to Tenant A |
Note
The IPsec rules control traffic coming from the remote tenant. On Tenant A, the source is Tenant B’s subnet; on Tenant B, the source is Tenant A’s subnet. Use protocol ‘Any’, rather than only TCP, so that ICMP and UDP traffic can also pass. Apply the rules on both tenants.
Configure Routing Gateways
Navigation: MTN Cloud VPN GUI → System → Routing → Gateways
MTN Cloud VPN automatically creates gateway entries based on the interface configuration. The critical requirement is that the LANGW (LAN gateway) entry points to the MTN Cloud VPN’s own LAN IP address. If the required gateway is not automatically created, create one.
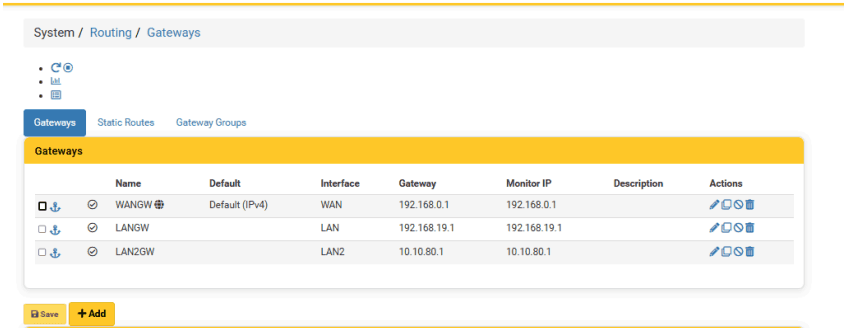
Figure 5 — Routing Gateways screen showing the WAN, LAN, and LAN 2 gateway entries and their associated interfaces and IP addresses
Configure the Linux VM Default Gateway
Navigation: VM Console
Log into the Linux VM console and add a route pointing to the MTN Cloud VPN LAN IP for the opposite site. Use the following command, replacing the placeholders with the appropriate destination network and gateway IP:
sudo ip route add <destination_network> via <gateway_ip> dev eth0
Allow Address Pairs on the Cloud Platform
Navigation: Cloud Platform → Networks → [LAN Network] → Ports → [MTN Cloud VPN eth1 Port] → Allowed Address Pairs
On the LAN network port associated with the MTN Cloud VPN eth1 LAN interface, add an allowed address pair for the entire LAN subnet. This allows any IP within the subnet to be sourced from the MTN Cloud VPN port.
| Field | Value |
|---|---|
| Port | MTN Cloud VPN eth1 / LAN interface port |
| IP Address | LAN subnet CIDR of the opposite tunnel |
Verify and Test the VPN Tunnel
Check Tunnel Status
Navigation: MTN Cloud VPN GUI → Status → IPsec
After applying the configuration, verify that both Phase 1 and Phase 2 show as Established.
| Status | Meaning |
|---|---|
| Established (green) | Tunnel is up and working correctly |
| Disconnected | Click Connect. If the connection fails, check that Phase 1 settings match on both sides |
| No phase 2 policies | Phase 2 network addresses are incorrect; check the subnet base addresses |
Ping Test from MTN Cloud VPN
Navigation: MTN Cloud VPN GUI → Diagnostics → Ping
Test connectivity from MTN Cloud VPN first. This helps isolate whether an issue is with the VPN tunnel or the VM configuration.
- On Tenant A MTN Cloud VPN, ping the Tenant B VM using Source: LAN.
- On Tenant B MTN Cloud VPN, ping the Tenant A VM using Source: LAN.
- If MTN Cloud VPN can ping both VMs, the tunnel is working correctly.
- If MTN Cloud VPN cannot ping the VMs, investigate the tunnel or firewall rules.
Ping Test from the VMs
Log into each Linux VM and test connectivity to the VM in the opposite tenant.
Site-to-Site VPN with Multiple LAN Interfaces and Multiple Phase 2 Entries
This configuration extends the site-to-site IPsec VPN deployment to support additional LAN interfaces and multiple Phase 2 entries. The additional network must be attached to the existing VPN VM, configured as an interface, and incorporated into the IPsec and firewall configuration.
Create the Additional Network
Navigation: Infrastructure → Networks → Create Network
Create the additional network required for the new LAN interface. Configure the following:
- Set Group to your tenant group.
- Enter a descriptive Name.
- Set the CIDR to the chosen private range.
- Input the Gateway.
- Check DHCP Server and Override IP so that IPs can be statically assigned.
- Click Save.
- Attach the router if the network is public-facing; otherwise, leave the network unattached to a router.
Reconfigure the VPN VM
Navigation: Provisioning → VPN VM → Action → Reconfigure
- Click Reconfigure.
- Click the + button beside Network.
- Select the additional network.
- Click Reconfigure.
- Confirm that the new interface has been added.
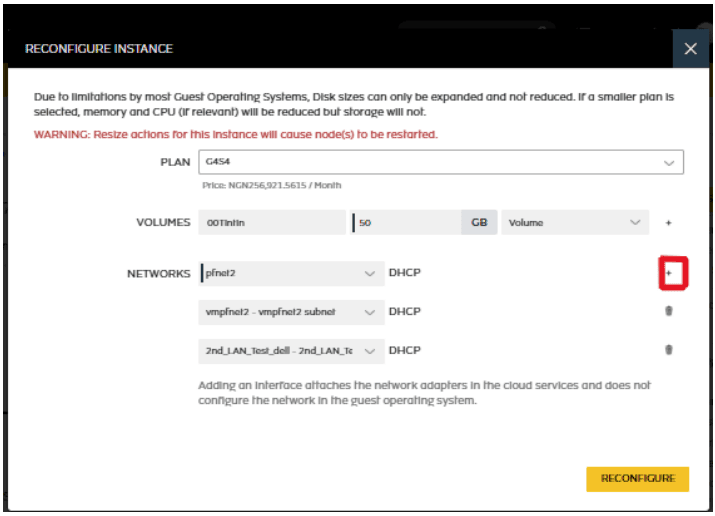
Figure 6 — VPN VM reconfiguration screen showing the option to add an additional network interface
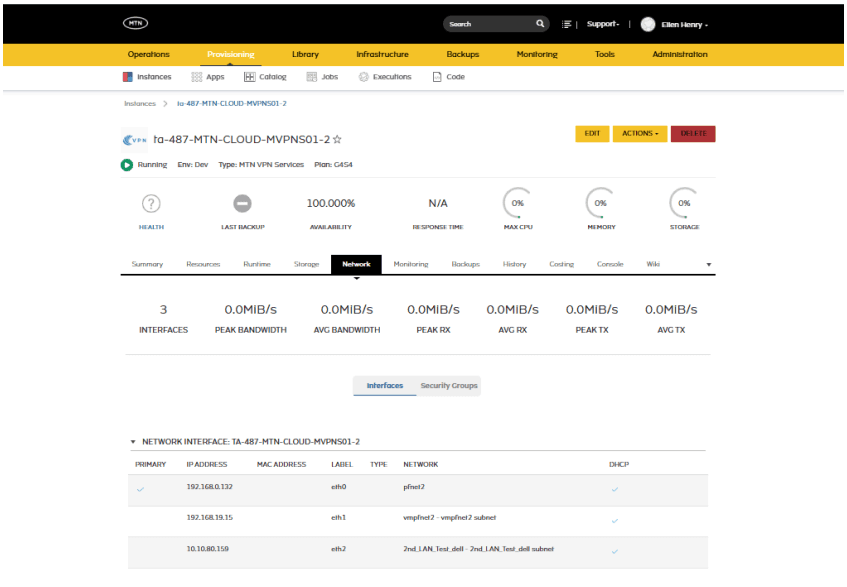
Figure 7 — Network selection and reconfiguration screen showing the additional network added to the VPN VM
Add the Interface
Navigation: VPN VM → Interface → Assignment
- Open the VPN VM web GUI.
- Log in using the configured credentials.
- Navigate to Interfaces.
- Select Assignments.
- Add a new interface.
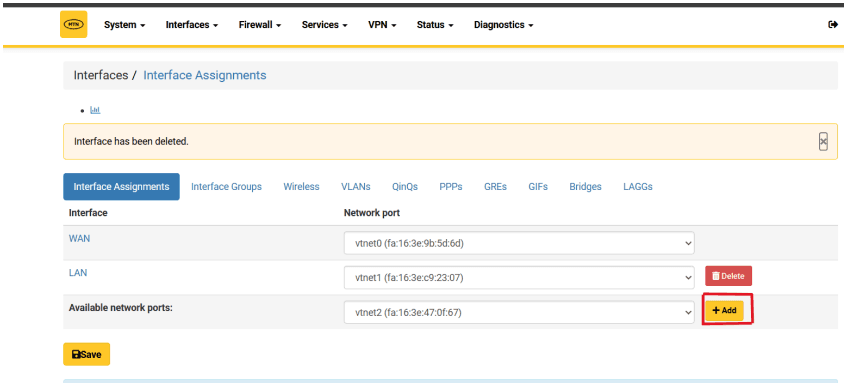
Figure 8 — Interface Assignments screen showing the process of adding a new LAN interface
- Edit the newly created interface.
- Enter the IPv4 address and Gateway.
- Select the Enable Interface option.
- Click Save & Apply Changes.
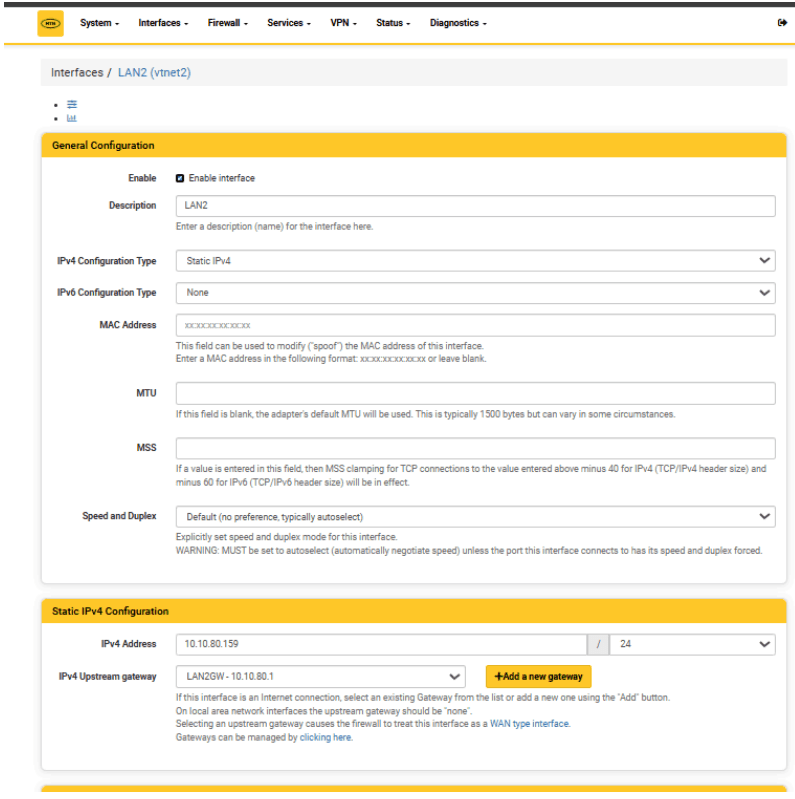
Figure 9 — New interface configuration screen showing the IPv4 address, gateway, and interface enablement settings
Configure IPsec Phase 1
Configure the IPsec Phase 1 settings for the additional tunnel.
Note: When the remote gateway has not previously been used in any tunnel, follow the Phase 1 configuration process referenced in the source material.
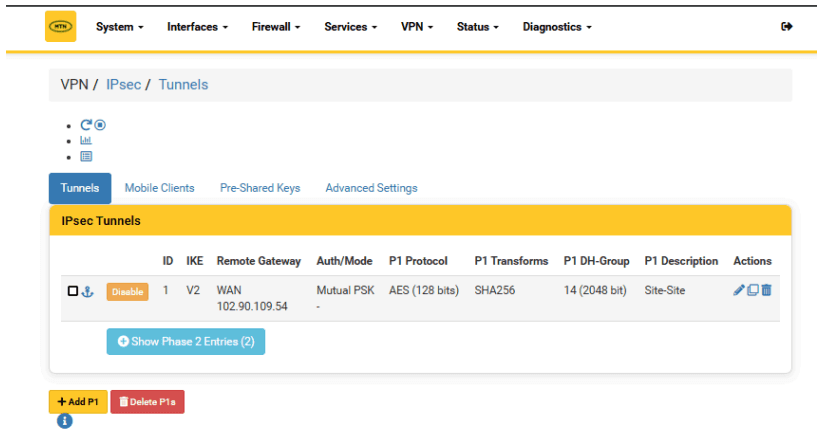
Figure 10 — IPsec Tunnels screen showing the configured Phase 1 tunnel and remote gateway
Configure IPsec Phase 2
Configure a new Phase 2 entry for the additional LAN network.
Note: When the local and remote gateways have already been used, begin from Phase 2. To create a new tunnel for the newly attached network, use a network that has not previously been used to create a tunnel for the local and remote sides.
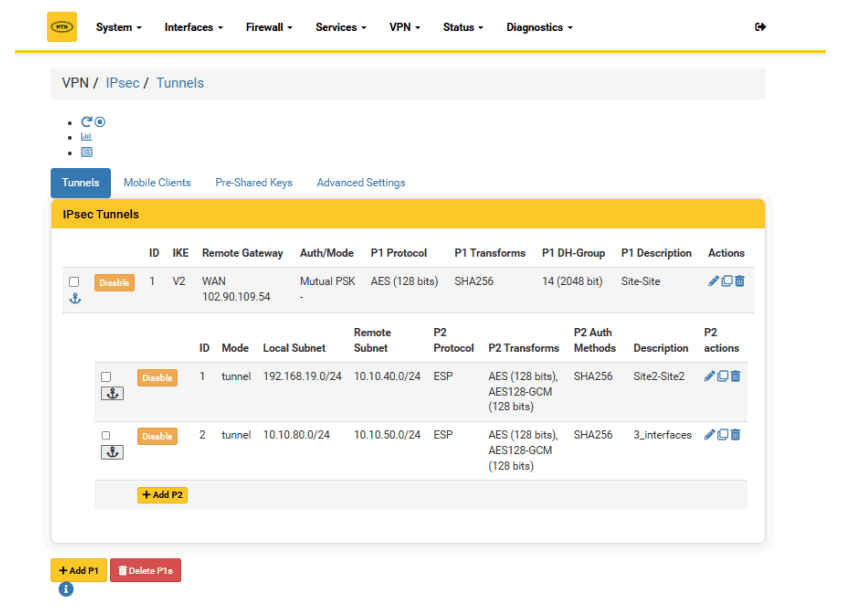
Figure 11 — IPsec Phase 2 configuration screen showing the additional local and remote network configuration
Configure LAN 2 Firewall Rules
Navigation: MTN Cloud VPN GUI → Firewall → Rules → LAN 2
Add the required rules to the LAN 2 tab for the additional network.
Configure IPsec Firewall Rules
Navigation: MTN Cloud VPN GUI → Firewall → Rules → IPsec
Add two rules to permit bidirectional traffic between the new subnets.
| Action | Protocol | Source | Destination | Description |
|---|---|---|---|---|
| Pass | IPv4 Any | 10.10.40.0/24 | 192.168.19.0/24 | Allow Tenant A to Tenant B |
| Pass | IPv4 Any | 192.168.19.0/24 | 10.10.40.0/24 | Allow Tenant B to Tenant A |
Note
The IPsec rules control traffic coming from the remote tenant. On Tenant A, the source is Tenant B’s subnet; on Tenant B, the source is Tenant A’s subnet. Use protocol ‘Any’, rather than only TCP, so that ICMP and UDP traffic can also pass. Configure the rules on both tenants.
Configure Routing Gateways
Navigation: MTN Cloud VPN GUI → System → Routing → Gateways
MTN Cloud VPN automatically creates gateway entries based on interface configuration. The critical requirement is that the LANGW gateway entry points to the MTN Cloud VPN’s own LAN IP address. If the appropriate gateway is not automatically created, create one. The additional LAN interface should also have its corresponding gateway configured.
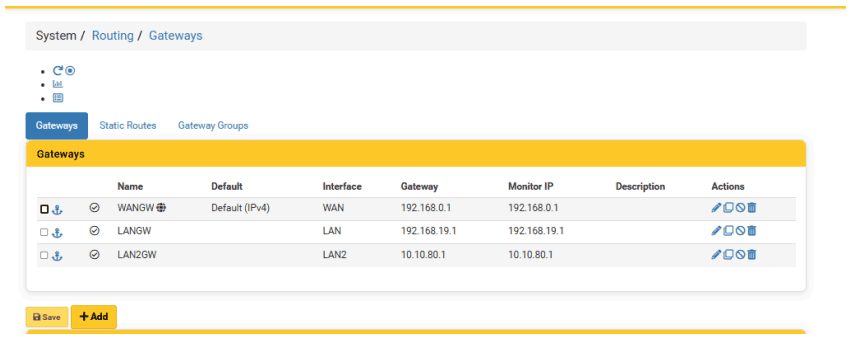
Figure 12 — Routing Gateways screen showing the WAN, LAN, and LAN 2 gateway entries for the multiple-LAN configuration
Set a Gateway
Navigation: VM via Console or SSH
Log into the Linux VM console and add a route pointing to the MTN Cloud VPN LAN IP for the opposite site. Use:
sudo ip route add <destination_network> via <gateway_ip> dev eth0
Allow Address Pairs on the Cloud Platform
Navigation: Cloud Platform → Networks → [LAN Network] → Ports → [MTN Cloud VPN eth1 Port] → Allowed Address Pairs
On the LAN network port associated with the MTN Cloud VPN eth1 LAN interface, add an allowed address pair for the entire LAN subnet. This allows any IP within the subnet to be sourced from the MTN Cloud VPN port.
| Field | Value |
|---|---|
| Port | MTN Cloud VPN eth1 / LAN interface port |
| IP Address | LAN subnet CIDR of the opposite tunnel |
Check Tunnel Status
Navigation: MTN Cloud VPN GUI → Status → IPsec
After applying the configuration, verify that both Phase 1 and Phase 2 show as Established.
| Status | Meaning |
|---|---|
| Established (green) | Tunnel is up and working correctly |
| Disconnected | Click Connect. If the connection fails, check that Phase 1 settings match on both sides |
| No phase 2 policies | Phase 2 network addresses are incorrect; check the subnet base addresses |
Ping Test from MTN Cloud VPN
Navigation: MTN Cloud VPN GUI → Diagnostics → Ping
Test connectivity from MTN Cloud VPN first to isolate whether an issue exists within the tunnel or the VM configuration.
- On Tenant A MTN Cloud VPN, ping the Tenant B VM using Source: LAN.
- On Tenant B MTN Cloud VPN, ping the Tenant A VM using Source: LAN.
- If MTN Cloud VPN can ping both VMs, the tunnel is working correctly.
- If MTN Cloud VPN cannot ping the VMs, investigate the tunnel or firewall rules.
Ping Test Across the Tunnel
Log into each VM and test cross-tenant connectivity through the newly configured tunnel.